
End-to-end automotive cybersecurity for connected and software-defined vehicles
Our automotive cybersecurity services help vehicle manufacturers, suppliers, and mobility innovators protect connected systems, ensure compliance with the ISO/SAE 21434 automotive cybersecurity standard, and deliver secure, resilient vehicles across the lifecycle.
As vehicles evolve into software-defined platforms, a robust automotive cybersecurity solution is essential to manage cyber risk, achieve certification, and access global markets.
Why automotive cybersecurity matters
The automotive cybersecurity market is rapidly expanding as modern vehicles integrate multiple connectivity layers, including Bluetooth, Wi-Fi, cellular networks, V2X, cloud platforms, and EV infrastructure.
This increased connectivity creates significant risks:
- Exposure to cyberattacks on safety-critical vehicle functions
- Greater dependence on secure software and OTA updates
- Increased vulnerabilities across global supply chains
- Mandatory compliance with ISO 21434, UNECE R155/R156, AIS 189/190, and other regulations
- Need for continuous monitoring and lifecycle risk management
Automotive cybersecurity must now be embedded across engineering, governance, and operations to ensure safety, compliance, and long-term resilience.
What is automotive cybersecurity?
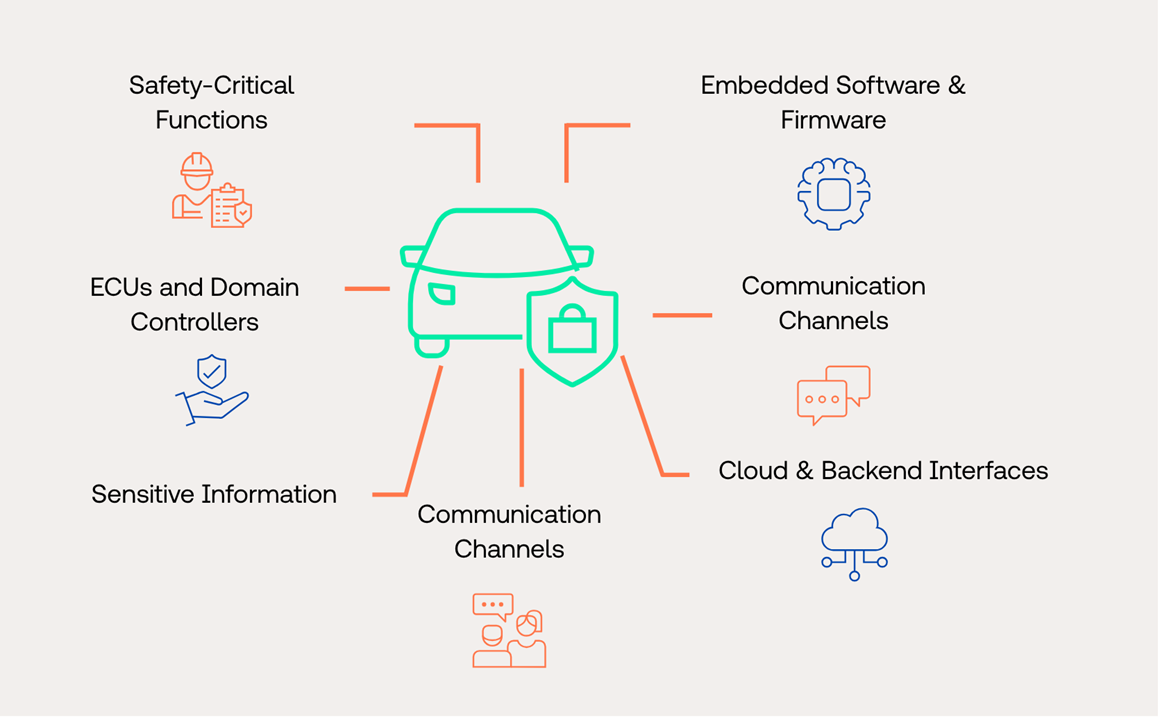
Automotive cybersecurity protects connected vehicles, electronic control units (ECUs), and in-vehicle systems from cyber threats.
It applies across the entire vehicle lifecycle, enabling secure development, validation, production, and post-deployment monitoring under frameworks such as the ISO/SAE 21434 automotive cybersecurity standard.
ISO/SAE 21434 automotive cybersecurity standard
The ISO/SAE 21434 automotive cybersecurity standard defines requirements for managing cybersecurity risks across road vehicle systems.
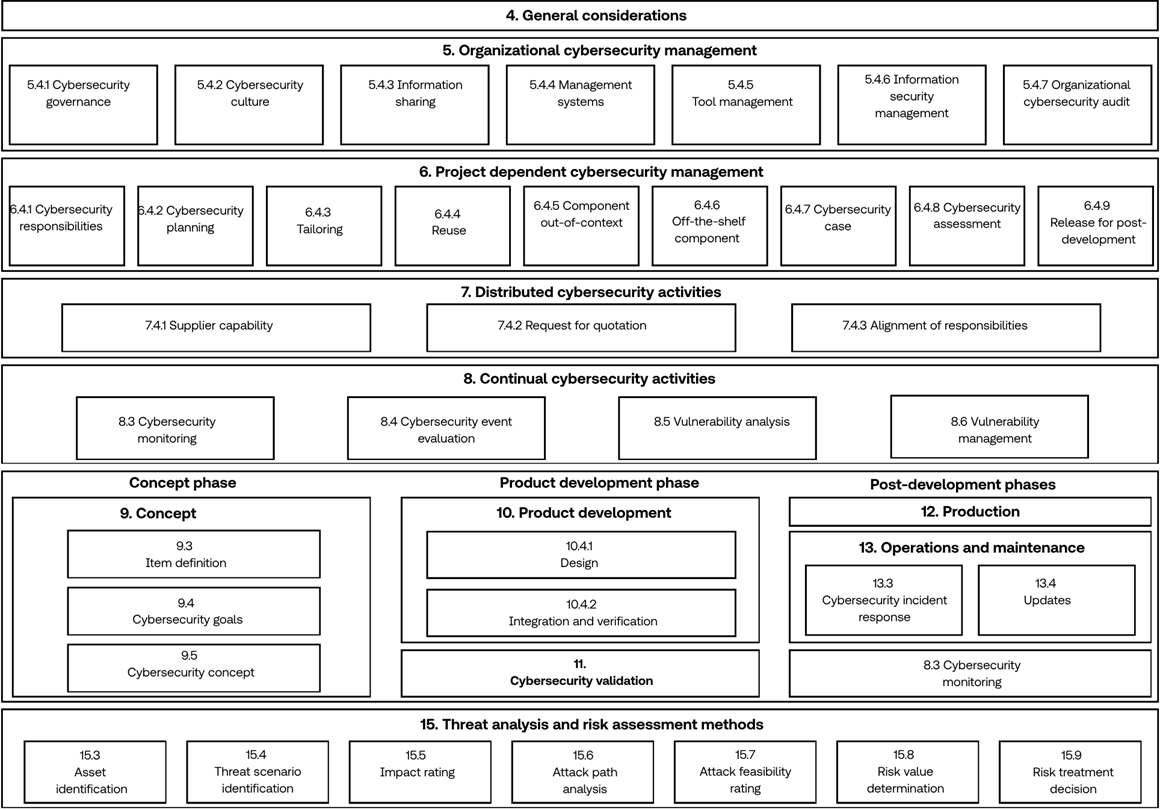
It enables organisations to:
- Integrate cybersecurity into product development lifecycle processes
- Perform structured Threat Analysis and Risk Assessment (TARA)
- Strengthen governance and supply chain security
- Achieve compliance and readiness for type approval
Achieving ISO 21434 certification demonstrates a robust cybersecurity management framework and supports global market access.
End-to-End automotive cybersecurity framework
We deliver a structured automotive cybersecurity solution across the entire vehicle lifecycle.
| Assess | Design | Implement | Monitor | Train |
| Establish visibility, maturity & risk baselines |
Build secure‑by‑design vehicle & component architectures |
Validate controls, test resilience & assure compliance |
Maintain cybersecurity throughout the vehicle lifecycle |
Build competence across engineering & governance teams |
Automotive cybersecurity services portfolio
Auditing & system certification
Cybersecurity Management System (CSMS) assessment
Based on UNECE R155 & ISO/SAE 21434, our CSMS assessment ensures your organisation:
- Implements cybersecurity governance across projects and functions
- Establishes secure development processes
- Maintains certification readiness for type approval
- Ensures compliance across the entire supply chain
- Technical security control verification
- Secure design review (architectural analysis)
Assessment outputs: Lifecycle weaknesses, critical risk elements, improvement recommendations.
Certification services
TÜV SÜD offers globally recognised certifications:
- ISO/SAE 21434 certification
- ISO 24089 certification
Conformity assessment services
- TISAX® assessment
- Combined cybersecurity & functional safety assessments (IEC 61508 / IEC 62443)
Cybersecurity services
Cybersecurity testing & validation services
Our advanced testing capabilities ensure robust protection of automotive systems.
- Vulnerability Assessment & Penetration Testing (VAPT)
- In‑vehicle systems VAPT
- ECU, gateway, telematics testing
- EV charger and charging infrastructure cybersecurity testing
- Compromise impact analysis
Fuzz testing & load testing
Stress and resilience testing for critical interfaces and communication channels.
Secure code review (SAST/DAST)
Evaluation of embedded software, firmware, interfaces, and middleware.
TARA development, review & validation
Structured Threat Analysis and Risk Assessment aligned with ISO/SAE 21434
Regulatory readiness for AIS 189 & AIS 190
India’s upcoming automotive cybersecurity and software update regulations require strong CSMS and SUMS capabilities.
AIS 189 (Cybersecurity)
We support:
- Organisational & technical cybersecurity readiness
- Risk assessments aligned with AIS 189
- Compliance documentation preparation
AIS 190 (Software Update Management System)
- Aligned with UNECE R156 & ISO 24089, covering:
- Secure OTA update validation
- Software integrity verification
- Version traceability and lifecycle monitoring
Software update engineering (ISO 24089)
Ensuring secure software update architecture and execution.
- Update campaign planning
- Integrity checks & rollback strategies
- Secure update infrastructure assessments
- Compliance with SUMS requirements
Training
Enabling organisations to develop internal expertise.
- Automotive SPICE based on 4.0 model
- Automotive Cybersecurity Practitioner
- SOTIF
- Automotive Functional Safety experts
- Foundation Trainings on TISAX
- E-mobility HV Trainings
- Automotive Core Tools
- OT Cybersecurity
- Automotive Foundation Level Penetration Tester
- Automotive Software Update Engineering based on ISO 24089
Who needs automotive cybersecurity services?
Our automotive cybersecurity services are designed for:
- Automotive OEMs
- Tier-1, Tier-2, and Tier-3 suppliers
- ECU, software, hardware, and system providers
- Organisations supplying to global OEMs
- Manufacturers and suppliers requiring compliance with AIS-189, AIS-190, ISO/SAE 21434, UNECE R155, and UNECE R156 requirements
Compliance with ISO 21434 and UNECE regulations is now essential for organisations operating in global automotive markets.
Why choose TÜV SÜD for automotive cybersecurity
- Global leader in automotive safety and cybersecurity
- Strong expertise in the ISO/SAE 21434 automotive cybersecurity standard
- Independent third-party certification authority
- Proven experience with connected and autonomous vehicles
- Integrated approach across safety, security, and compliance

Frequently asked questions (FAQs)
What is automotive cybersecurity?
Automotive cybersecurity protects vehicles from digital attacks that target electronic control units (ECUs), in-vehicle networks, wireless interfaces, and software systems. It secures connected, autonomous, and electric vehicles by managing risks across design, development, production, and over-the-air updates under standards such as ISO/SAE 21434 and UNECE R155.
What is automotive cybersecurity certification?
Automotive cybersecurity certification confirms compliance with ISO/SAE 21434, ISO 24089, TISAX®, and regulatory frameworks such as UNECE R155/R156 and AIS 189/190.
What is TARA in automotive cybersecurity?
TARA (Threat Analysis and Risk Assessment) identifies threats, assesses attack paths, and defines security controls to reduce vehicle cybersecurity risk under ISO/SAE 21434.
What is AIS 189 and how does it impact automotive manufacturers in India?
AIS 189 mandates cybersecurity risk management, secure development, documented compliance, and audit readiness for vehicle approval in India.
What is required for compliance with AIS 190 Software Update Management System regulations?
AIS 190 compliance requires a UNECE R156-aligned SUMS that secures OTA updates, verifies software integrity, maintains traceability, controls infrastructure, and documents processes for audit and approval.

